CBUAE AML Fine: a Branch, its MLRO, and what the role now carries

A branch, a fine, and a second penalty
On 24 June 2026 the Central Bank of the UAE fined a branch of a foreign bank AED 20 million. The release cites "significant, repeated failures" in the branch's framework for anti-money laundering, counter-terrorist financing, and illegal organisations and sanctions. The legal basis is Article 137 of Federal Decree-Law No. 14 of 2018, the law that governs the Central Bank.
On its own, that number would not be news. Institutional fines at this scale are not new in the UAE. Just in May 2025 an exchange house paid AED 200 million. What sets June apart is the second penalty, and one word in the first.
The person stays anonymous. The role does not.
A separate penalty of AED 300,000 was imposed on the branch's Head of Compliance and Money Laundering Reporting Officer.
The CBUAE named neither the branch nor the officer, in line with its usual practice. That is the detail worth sitting with. The person stays anonymous. The role does not.
The release sets out the individual penalty as a finding in its own right, which means the MLRO seat now appears in UAE enforcement as its own category of liability, separate from the institution's.
What "repeated" tells you
The regulator's stated reason for the individual penalty runs to a single clause: failure to fulfil his responsibilities and position functions. It did not elaborate, and the specific conduct has not been made public.
What is public is the word "repeated." Examiners had been in before, findings were raised, and those findings were still live when examiners returned.
In most firms, the MLRO is the officer who owns the remediation plan and reports on whether it has landed. That is the structural reason an institutional finding can attach to one person, and it is worth testing against your own governance regardless of what happened at this particular branch.
Why personal liability is written into the law
Personal liability is not a passing mood at the regulator, it is written into the law.
Federal Decree-Law No. 10 of 2025 came into force on 14 October 2025, replacing Decree-Law 20 of 2018, with Cabinet Resolution 134 of 2025 as its executive regulation.
The material shift is a "should have known" standard for senior managers and compliance officers, where knowledge can be inferred from circumstances rather than proven directly.
Article 137 of Federal Decree-Law No. 14 of 2018 is the penalty basis the CBUAE relies on, and it has been used against individuals before.
In the May 2025 exchange house case, the branch manager wasn't only fined AED 500,000, he was permanently banned from the UAE financial sector.
June adds the compliance officer to that precedent.
The eighteen months nobody examines
A remediation plan is written against the firm you were on the day of the examination. The problem is that nothing about your client base agrees to stay still afterwards.
A client onboarded as low risk in 2023 takes a government advisory role in 2025. The file did not change, so nothing re-scores. A UBO structure gets restructured through a new jurisdiction and the risk rating still reflects the old chain.
A monitoring rule set tuned to last year's transaction patterns quietly stops matching this year's. None of that shows up in a policy review, because the policy is still correct. The control just isn't doing what the policy says any more.
Periodic review is the usual answer, and it is the reason findings reopen. On an annual cycle, you learn about a change up to twelve months late. On a triennial cycle for low-risk clients, thirty-six. An examiner arriving in month twenty does not care which month of your cycle they caught you in.
azakaw re-scores on events rather than on the calendar. Screening runs continuously against updated lists, a material change to a client or its ownership re-triggers the risk rating, and a rating change routes into review automatically.
The framework notices drift before an examiner does, and every re-score leaves a dated record showing it noticed.
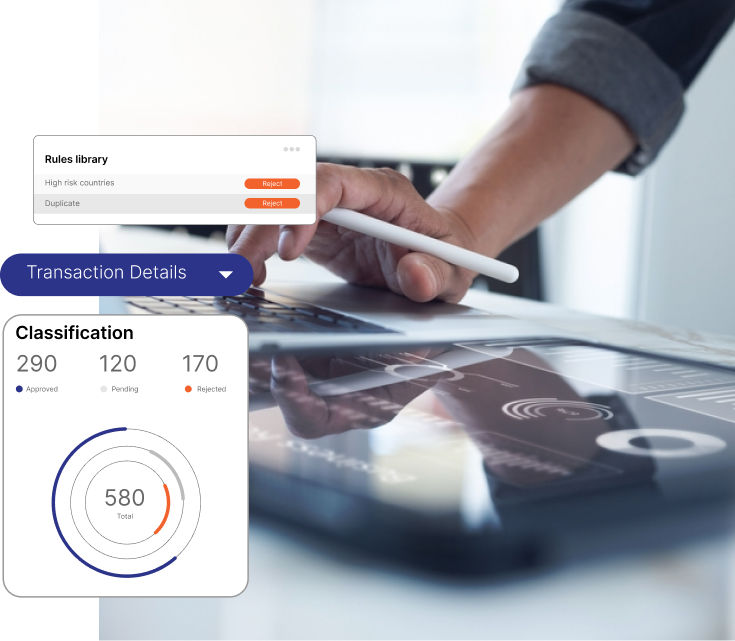
Automated Risk Intelligence
Move away from rigid calendar schedules. azakaw re-scores clients instantly when ownership or data shifts, routing changes straight to review and logging a dated audit trail of every check.
Where a repeated finding comes from, and what closes it
A repeated finding rarely comes from one bad decision. It builds up where the work and the record of the work drift apart. Here are five places that happens, and what azakaw does at each.
Where it breaks | What azakaw does |
Examination findings stay open, or close on paper only | Corporate Compliance assigns and tracks tasks across the organisation, with automated due-date alerts, a built-in calendar and customisable approval workflows |
Client risk drifts between reviews | After approval, the whole customer database is monitored daily, with adverse media checked four times a day. Real-time alerts flag changes in the risk profile of a business, its owners or directors, including sanctions, PEP and negative news updates. Risk scoring is dynamic |
Monitoring rules fall out of step with the business | Transaction Monitoring runs on a customisable rules engine, with thresholds and workflows set to your organisation |
Decisions can't be reconstructed | Case management with escalation and note-taking keeps complete case histories |
Evidence is assembled after the examiner arrives | Comprehensive audit reports are generated from the platform in a few clicks, in PDF |
The MLRO still makes the call. What changes is that the call, and the record behind it, can be shown.
The evidence pack: what to have ready before day one
When examiners return, they don't ask whether you have a policy. They ask you to show them it worked.
On the first morning, an MLRO should be able to put six things on the table:
The remediation log from the last examination, with status, owner and evidence for each finding
The risk rating history for any client they sample, with the date and trigger for each change
Screening history since onboarding, not just the result at onboarding
The trail from alert to decision for sampled cases, including escalations and STR filings
The monitoring rule change log, with the reason and testing behind each change
The management information you gave senior management, and what they decided
If the work runs through one system, every item on that list is a by-product of the work. If it doesn't, each item is a separate project, started the week the examiners call.
Five questions to ask this week
You don't need a platform to start. You need honest answers to these:
How many findings from your last examination are formally closed, and could you show the evidence for each within a day?
When a client's ownership or role changes, how long before its risk rating changes too?
When did someone last test whether your monitoring rules still match how your clients transact?
If an examiner picked ten cases at random, could you rebuild every decision without asking the analyst who made it?
What did senior management last see about the programme's effectiveness, and is their response on file?
If any answer starts with "it depends who you ask", that's where to begin.
The June release left the officer unnamed. It still made its point about the role. If you want to test your answers against a working framework, book a walkthrough with the azakaw team and bring your last examination report. We'll show you how each finding would run from open to evidenced.
Which of the five would take your team longest to answer?

Built on UAE Deep Expertise
Verify customers and businesses, detect suspicious identities and strengthen AML compliance with azakaw. Leverage the most advanced AI technology to safeguard your business from fraud and fines.
Sources
CBUAE imposes a financial penalty of AED 20,000,000 on a branch of a foreign bank, Zawya, 24 June 2026
CBUAE AML Fine: a Bank, Its MLRO, and a Warning, Zyphe
UAE Central Bank Fines Foreign Bank and Compliance Officer, Global Investigations & Compliance Review
CBUAE imposes a financial sanction of AED 200 million on an exchange house, CBUAE, 20 May 2025
UAE AML Law 2025: Federal Decree-Law No. 10, Zigram
UAE's AML framework under Cabinet Resolution No. 134 of 2025, Al Tamimi & Company
UAE's New AML Law: A reset for corporate accountability, Clyde & Co